Skip to content

Security and governanceBrief

LLM gateway security architecture: one enforceable boundary

A gateway adds a party to the data path, but it also creates one place to enforce credentials, model policy, budgets, logging, and provider access.

By INFRO Editorial

Published

Updated

1 min read

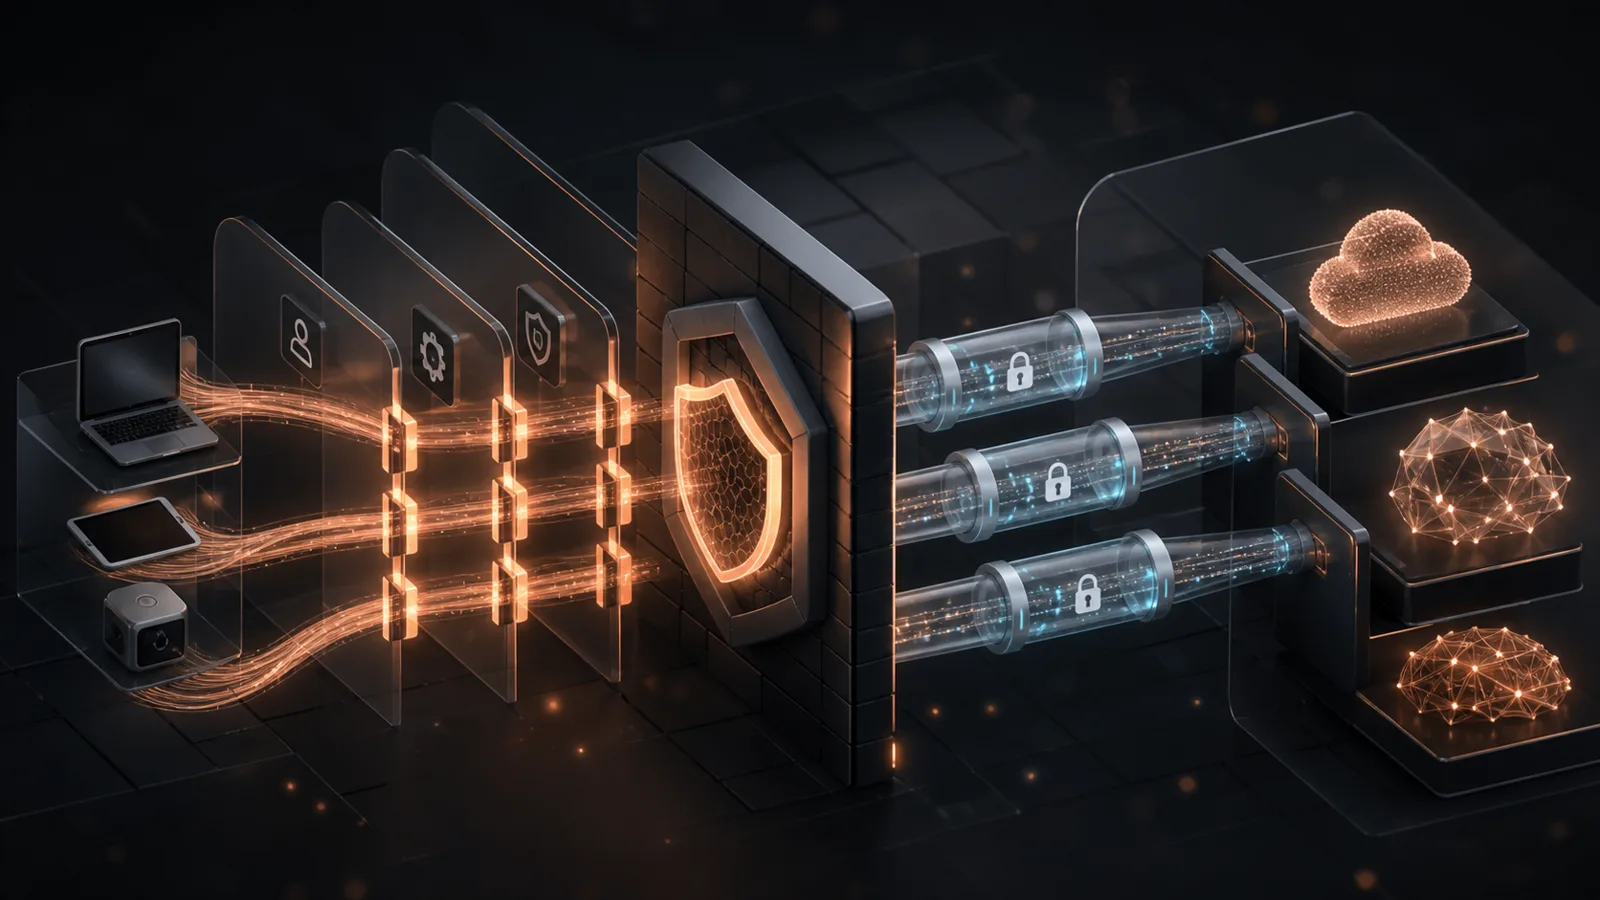
Layered secure architecture protecting AI traffic as it crosses a single gateway boundary

In short

An LLM gateway is both a data-path dependency and a security enforcement point. A sound architecture minimizes retained content, scopes credentials, controls models and providers, protects logs, isolates tenants and environments, audits changes, and publishes the processors and policies buyers need to assess.

Map the complete data path

Document application, gateway, provider routes, logs, analytics, support tooling, backups, and media storage. For each hop, identify data, purpose, region, encryption, retention, deletion, and access.

A gateway does not remove provider review; it should make the active provider path visible and reduce direct credentials in applications.

Centralize enforceable policy

Use scoped keys, projects, roles, model allowlists, spend ceilings, rate controls, and environment separation. Apply policy before forwarding a request so disallowed data or models do not reach an upstream route.

Keep agent tool permissions separate. Permission to call a model is not permission to send an email, transfer money, or delete data.

Protect operational evidence

Request traces are sensitive because metadata can reveal customers, features, and usage patterns even without prompts. Restrict access, redact secrets, choose retention deliberately, and audit privileged reads and policy changes.

Default to metadata-first logging and enable payload capture only for an approved debugging or evaluation purpose.

Evaluate the vendor honestly

Review security documentation, DPA, subprocessors, incident process, vulnerability handling, deletion, availability, and current certifications. Test key revocation, model restrictions, error behavior, and log access.

Separate implemented controls from roadmap promises. Procurement needs the current state.

From the team that builds it

Where this shows up in INFRO

INFRO is a control plane in front of the provider accounts you already hold. The capabilities below are the parts of it this article touches, each with the documentation that defines its behaviour.

INFRO accounts are self-serve. Provider usage is billed to you by your providers; INFRO charges a software subscription and takes 0% of model spend. See plans.

About this article

Last checked against its sources on . The next review is due by . No separate named reviewer is recorded for this article.

How articles are written, sourced and corrected is set out in the editorial standards.

Revision history

  1. Removed the promotional template sections and the generic FAQ, moved product context into the product section, and corrected product wording to the current BYOK model.